
Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Understanding Adversarial Attacks on AI Models
In the rapidly changing realm of AI, being proactive against adversarial attacks is essential to safeguard the security and reliability of our models. With our comprehensive defense guide, we equip you with the knowledge and techniques necessary to thwart these attacks.
Popular right now

Breville Barista Express Espresso Machine with Built-In Grinder, Brushed Stainless Steel

De'Longhi COM630BK All-in-One Coffee and Espresso Machine

Philips 2300 Series Fully Automatic Espresso Machine with LatteGo
As an affiliate, we earn on qualifying purchases.
Exploring Common Types of Adversarial Attacks
Adversarial attacks exploit vulnerabilities in AI systems, aiming to deceive or manipulate their outputs. Understanding these attack strategies is crucial for developing robust defense mechanisms to proactively identify and mitigate their impact.
Strategies to Safeguard AI Models
Implementing countermeasures like adversarial training, input sanitization, and model ensembling can enhance the accuracy and robustness of AI models against adversarial threats. Continuous monitoring and updating of defense mechanisms are also crucial.
Real-World Adversarial Attack Case Studies
Real-world examples like ‘image poisoning’ and ‘model evasion’ attacks highlight the vulnerabilities of AI models and the importance of proactive defense strategies. Mitigating these attacks requires a combination of techniques to stay ahead of threats.
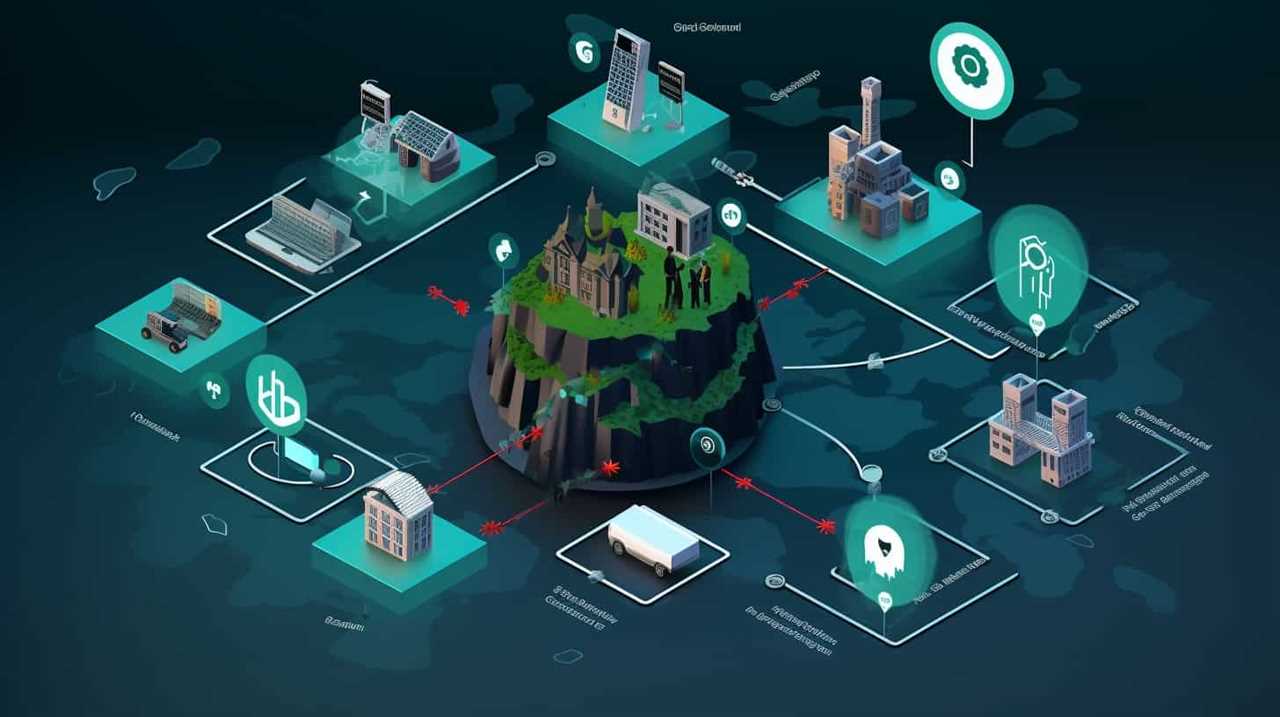
Responding to Adversarial Attacks in Real-Time
Monitor, detect, and analyze adversarial attacks in real time to minimize potential damage. Implementing real-time response strategies and leveraging advanced detection techniques can effectively safeguard AI models against evolving threats.
Best Practices for AI Model Security
Implementing best practices like regular updates, multiple layers of defense, strong access controls, and continuous monitoring can enhance the resilience of AI models against adversarial attacks. Training and awareness programs for the development team are also vital.
Legal and Ethical Implications of Adversarial Attacks
Potential legal implications of adversarial attacks on AI models include liability issues, privacy breaches, and regulatory compliance. Addressing biases, discrimination, and trust erosion in AI systems is crucial for ethical considerations.
Conclusion: Ensuring Integrity and Reliability of AI Models
By implementing robust defense mechanisms, staying proactive, and deploying best practices, we can confidently navigate the evolving landscape of adversarial attacks and ensure the security and reliability of our AI models.