TL;DR

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
PHP issued emergency updates for two critical vulnerabilities that can enable unauthenticated remote code execution on affected web deployments. The Dutch government said Overheid.nl, MijnOverheid.nl and DigiD were taken offline as a precaution on Oct. 21; it did not report confirmed compromises. Operators need to update the PHP runtime and verify the web-facing service is using the patched version.
PHP released emergency fixes on Oct. 21 for two critical flaws that can allow unauthenticated attackers to execute code remotely, and the Dutch government said it took Overheid.nl, MijnOverheid.nl and DigiD offline as a precaution. The government announcement did not say the sites had been compromised, while PHP urged operators to update the runtime serving their websites.
The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619 and collectively described as PHP2Shell, affect PHP installations handling web requests. PHP lists PHP-FPM, Apache mod_php, php-cgi, FrankenPHP and LiteSpeed among the potentially affected configurations. The two advisories each assign a CVSS v4.0 score of 9.2, Critical.
PHP’s advisory describes one flaw involving interrupted memory handling after an out-of-memory failure: cleanup may treat partly initialized request data as valid, creating memory corruption that can lead to code execution. The other flaw involves internal state retaining references to memory that has already been freed; a later request handled by the same worker may use those stale references. PHP says both issues can lead to remote code execution, but exposure depends on the deployment and configuration.
Fixes were released for PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP also provided minimal source backports for versions 7.4, 8.0 and 8.1, which are outside normal upstream support. Operators using older versions or vendor-maintained packages need to confirm with their provider that both vulnerabilities are addressed; a version string alone may not show whether a backport is present.
Security briefing · October 21
PHP2Shell Puts Critical PHP Vulnerabilities In Focus As Dutch Sites Go Offline
PHP issued emergency fixes for two critical flaws that can enable unauthenticated remote code execution. Dutch public websites were taken offline as a precaution; the announcement did not report confirmed compromise.
Two paths to code execution
The advisories describe flaws in PHP installations handling web requests. Exposure depends on deployment details and configuration.
Interrupted cleanup
After an out-of-memory failure, cleanup may treat partly initialized request data as valid. The resulting memory corruption can lead to code execution.
Freed memory reused
Internal state can retain references to memory that has already been freed. A later request handled by the same worker may use those stale references.
Web-facing PHP
PHP lists PHP-FPM, Apache mod_php, php-cgi, FrankenPHP, and LiteSpeed among the configurations to assess.
Fix the engine, then verify it
Identify the PHP runtime actually serving production, staging, and legacy sites. A version string alone may not reveal a vendor backport.
Deploy the applicable fixed release, complete any required restart or redeployment, and verify that live requests reach the patched runtime. Check that site functions still work.
For older or vendor-maintained packages, ask the provider to confirm that both CVEs are addressed. PHP provided minimal source backports for versions outside normal upstream support.
A precautionary shutdown
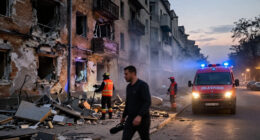
The Dutch government said several services were taken offline on October 21 after the vulnerability disclosure.
Offline as a preventive measure
The government named Overheid.nl, MijnOverheid.nl, and DigiD. The announcement described a precautionary shutdown and did not report confirmed compromise.
These services support public information and government-related online access, so taking them offline can interrupt access even without a confirmed breach.
Not reported: confirmed compromise or return-to-service time
“Several websites, including Overheid.nl, MijnOverheid.nl and DigiD, were taken offline as a precaution on Oct. 21.”Dutch government
“The vulnerabilities affect installations handling web requests,” including several PHP serving configurations.PHP security advisory
“The vulnerabilities can lead to remote code execution.”PHP security advisory
Patch, verify, review
Patching matters, and it cannot undo an intrusion that may have happened earlier. Preserve relevant logs and investigate suspicious activity.
Inventory
Find production, staging, and legacy deployments handling web requests.
Patch
Install a listed fixed release or a vendor-confirmed package covering both CVEs.
Confirm
Restart or redeploy as needed; verify live traffic uses the patched runtime.
Review logs
Preserve relevant records and investigate suspicious activity while patching.
Evidence has limits
The source material leaves key questions open. Keep the distinction between reported activity, confirmed compromise, and technical possibility clear.
Were the Dutch sites confirmed hacked?
No confirmed compromise was reported in the described government announcement. It said the services went offline as a precaution.
Is every PHP server equally exposed?
No. Attack paths depend on deployment details. Advisories describe demonstrated exploitation on Apache with mod_php; research also describes application-dependent paths involving PHP-FPM.
Does the score prove a breach?
No. A CVSS 9.2 score rates severity; it does not establish successful exploitation, compromise, or equal exposure across configurations.
When will the services return?
The source material gives no return-to-service timetable or further government update schedule.
Why PHP Runtime Updates Matter
The flaws affect the PHP engine, so updating a site’s content management system, theme or plugins does not by itself install the security fix. Operators need to identify the PHP runtime used by live sites, staging systems and older applications, then deploy a fixed release or a vendor-confirmed patched package.
PHP says demonstrated attacks on Apache with mod_php can occur before application code runs. Its advisory also says execution occurs as the web worker account; that does not automatically mean an attacker gains administrator or root access. The severity makes prompt patching important, but the score alone does not establish that every configuration is equally exploitable.
PHP warns that applying a patch cannot undo an intrusion that may have happened earlier. Operators should preserve relevant logs and investigate suspicious activity while patching. A web application firewall can add protection, but PHP describes it as an extra layer rather than a substitute for updating the runtime.
As an affiliate, we earn on qualifying purchases.
How the Dutch Shutdown Fits
The Dutch government named Overheid.nl, MijnOverheid.nl and DigiD among the sites taken offline on Oct. 21 as a preventive measure following the PHP vulnerability disclosure. These services support public information and government-related online access, so taking them offline can interrupt access even when no breach has been confirmed. The announcement described a precautionary shutdown, not evidence that attackers had accessed those services.
Cloudflare separately reported attack attempts against its customers. That report indicates activity related to the flaws, but the source material does not establish that the Dutch sites were targeted or that those attempts succeeded. PHP’s security team led the fixes and releases. Calif, OpenAI and Wiz described AI-assisted research that helped researchers identify the flaws; the available account also says expert investigation and deployment work remained necessary.
“Several websites, including Overheid.nl, MijnOverheid.nl and DigiD, were taken offline as a precaution on Oct. 21.”
— Dutch government
PHP web server vulnerability patch
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
What Is Known About Exposure
The source material does not establish whether the Dutch government sites were compromised, whether attackers specifically targeted them, or when they would return to service. It also does not provide the number of affected PHP installations or confirm the extent of successful exploitation elsewhere.
PHP says attack paths depend on deployment details. The advisories describe demonstrated exploitation on Apache with mod_php, while Calif’s technical research describes application-dependent paths involving PHP-FPM. That information does not establish that every server running those technologies is vulnerable in the same way. Code execution as a web worker also does not, by itself, establish access to the wider system with administrator privileges.
As an affiliate, we earn on qualifying purchases.
Patch, Verify and Review Logs
Website operators should inventory production, staging and legacy deployments; identify the PHP version actually serving web requests; and install the applicable fixed release or package confirmed by their vendor. They should complete any required restart or redeployment, then verify that live requests reach the patched runtime and check that site functions work.
Organizations that cannot patch immediately should discuss access restrictions or temporary offline operation with their provider. PHP advises keeping relevant protections enabled, while treating configuration mitigations as limited to particular attack paths. Operators should also review and preserve relevant logs for signs of suspicious activity. The source material gives no return-to-service timetable for the Dutch sites or further government update schedule.
As an affiliate, we earn on qualifying purchases.
Key Questions
What are the PHP2Shell vulnerabilities?
They are two PHP flaws tracked as CVE-2026-109618 and CVE-2026-109619. PHP says they can lead to unauthenticated remote code execution in affected web deployments.
Were the Dutch government websites confirmed to be hacked?
No confirmed compromise was reported in the government announcement described in the source material. It said Overheid.nl, MijnOverheid.nl and DigiD were taken offline as a precaution.
Which PHP releases contain the fixes?
The listed fixed releases are 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP also provided minimal source backports for 7.4, 8.0 and 8.1; users of vendor packages should confirm that both CVEs are addressed.
Does updating WordPress fix these vulnerabilities?
No. These flaws affect the PHP runtime. Updating WordPress, themes or plugins alone does not install the PHP engine fixes.
Does a critical severity score mean every site is equally exposed?
No. PHP assigns each flaw a CVSS v4.0 score of 9.2, Critical, but says exposure and attack paths depend on deployment and configuration.
Source: Thorsten Meyer AI
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.